version 2.4.8 du 31/08/2026
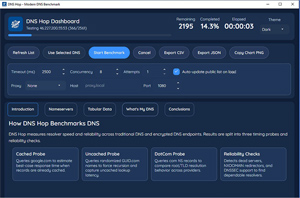
- IP version selector (#6). Choose whether a run covers Both, IPv4 or IPv6. Picking IPv4 skips the resolvers addressed by an IPv6 literal, which keeps them out of the results on connections without IPv6 rather than listing them all as dead. Picking IPv6 tests only those endpoints. Resolvers reached by hostname are not tied to an address family, so they stay in the Both and IPv4 runs.
- DNSSEC toggle (#7). The DNSSEC check can now be turned off. When it is off the validation probes are skipped entirely, which saves up to two queries per resolver on a large run, and the diagnostics log records the check as skipped rather than reporting a lack of support.
version 2.4.7 du 27/08/2026- DNSSEC detection : DNSSEC support has always been measured live rather than maintained by hand: each run asks the resolver for a domain published with a deliberately broken signature, and a resolver that validates refuses to return it. What went wrong was how a missing answer was read.
- DNSSEC detection : No answer is no longer treated as "no DNSSEC". That probe runs last, after a dozen or more queries against the same resolver, so on a busy run it was the one most likely to be squeezed out by a slow or rate-limiting server. Silence was being recorded as a lack of support, which is why a provider could appear to validate on one of its addresses and not on another. An inconclusive probe is now retried on a fresh connection with a longer timeout.
- DNSSEC detection : Validation is now confirmed against a correctly signed control domain, so a resolver that is failing every query cannot be mistaken for one that is rejecting bad signatures. The "authenticated data" flag is deliberately not used as the deciding signal, because at least one large provider sets it while still returning the broken signature.
- DNSSEC detection : A dropped DNS-over-TLS session is retried on a fresh connection. Previously every remaining probe on that server failed once the resolver closed the connection.
- DNSSEC detection : Verified against thirteen resolvers with known behaviour, including confirmation that Level 3, Comodo and 114DNS genuinely do not validate.
- EDNS Client Subnet tester : Results now show an ECS badge for resolvers that honour EDNS Client Subnet (RFC 7871), and the flag is included in CSV and JSON exports. The app sends a client subnet option and reports whether the resolver echoes it back, which is what separates a resolver that takes the client's network into account from one that ignores it. Works over plain DNS, DoH and DoT.

 (0 votes)